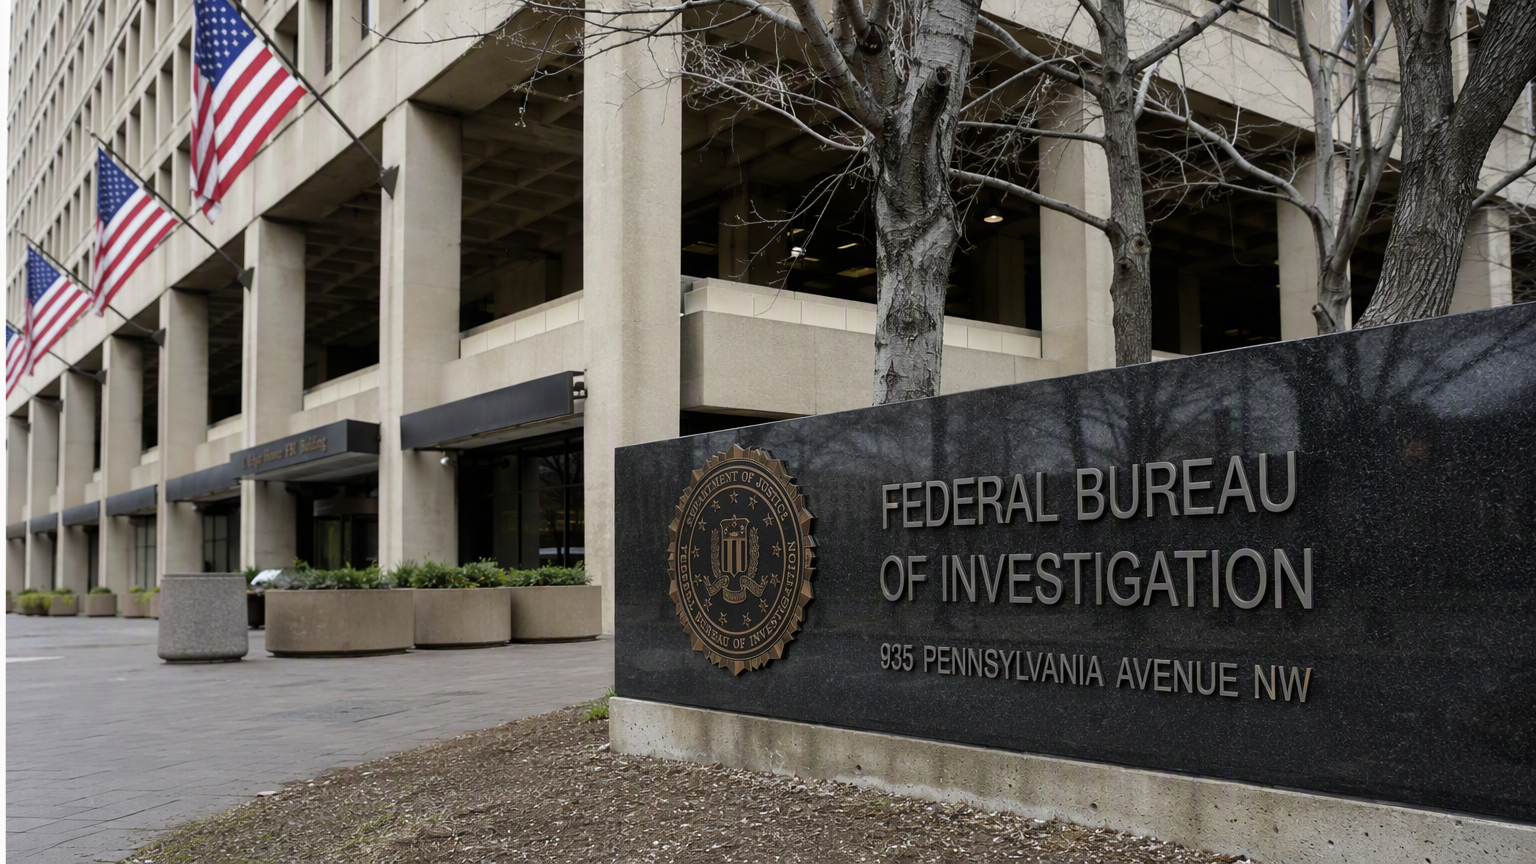
Some hackers walked up, knocked on the FBI’s digital front door, and apparently just… let themselves in. That’s the claim anyway. A group is now saying they’ve got personal data on every single FBI employee, and if that’s true, this isn’t just another breach headline to scroll past. This is the kind of thing that should make a lot of people very nervous, very fast.
Wait, All of Them?
Let’s sit with that for a second. Not “some employees.” Not “a database from 2019 that nobody patched.” All of them, according to the hackers themselves, who apparently announced this with the subtlety of a group that wants credit. The post making the rounds is literally titled “We Hacked the FBI,” which, I mean… that’s not exactly a headline you bury.
Now, do I believe every word of a hacker’s self-promotional claim at face value? No. Not really. Hackers exaggerate. It’s basically part of the job description at this point – you breach something, then you inflate the story a little to make yourselves look scarier and smarter than you maybe are. But here’s the thing: even a partial version of this being true is bad. Like, genuinely bad. We’re talking about an agency where employees’ identities being exposed isn’t just embarrassing, it’s potentially dangerous for undercover agents, for ongoing investigations, for people whose entire safety depends on nobody knowing who they are or where they live.
The Data in Question
From what’s being reported, we’re talking about the kind of personal information you’d expect – names, contact details, internal identifiers, that sort of thing. It’s not entirely clear yet how deep this goes, and honestly, that ambiguity is almost worse than a clean confirmed number. When you don’t know the scope, your brain just fills in the worst-case scenario. And in this case, the worst case involves federal agents.
How Does Something Like This Even Happen?
This is where I get a little worked up, not gonna lie. We are talking about the Federal Bureau of Investigation. The agency that investigates cybercrime. The agency that shows up after a company gets hacked and tells them what they did wrong. If it turns out their own systems had a hole big enough to drive this through, that’s not just ironic, that’s a real problem with how seriously internal security gets treated even at the highest levels of government.
I’ve seen this pattern before, actually – big institutions assume their name and reputation are a kind of shield. Like, “who would dare target us.” But that logic has never made sense to hackers. If anything, targeting a huge, high-profile institution is the whole appeal. You get the story, the notoriety, and depending on what you took, potentially something valuable to sell or leverage later.
“We hacked the FBI” isn’t a sentence you expect to read outside of a movie script, and yet here we are.
The Part Nobody’s Really Talking About
Everyone’s focused on the scale of this – all employees, wow, huge number, scary headline. But what’s interesting here, and kind of gets buried, is what this means for the individuals involved. These aren’t anonymous line items in a spreadsheet. These are real agents, analysts, support staff, people with families, people who maybe worked cases against actual dangerous people. If their personal info is floating around in some hacker forum or getting sold on the dark web, that’s not an abstract “data breach” problem. That’s someone’s home address potentially in the wrong hands.
And look, breaches happen constantly. We’ve all become a little numb to them, if I’m being honest. Another day, another company saying “we take your privacy seriously” right after failing to protect it. But this one feels different because of who the victim is. The FBI is supposed to be the response team, not the case file.
What We Still Don’t Know
- Whether the claim is fully verified or partially exaggerated
- The actual method used to get in
- How long the access existed before anyone noticed
- What, if anything, is actually being done with the data right now
That last one is probably the scariest part. Data sitting quietly is one thing. Data being actively used – for harassment, targeting, blackmail, whatever – is a whole different level of bad.
What This Actually Means
Here’s my honest take. Whether this claim turns out to be 100% accurate or somewhat inflated, the fact that it’s even plausible enough to spread this fast tells you something. People believe it could happen. And when the public’s default reaction to “hackers breached the FBI” is more “yeah, that tracks” than “no way,” that says a lot about where we are with institutional trust and cybersecurity right now.
I’ll be watching to see if the FBI puts out an actual statement addressing the scope directly, because so far the silence (or vague non-denial, depending on what comes out) is doing more damage than a clear answer would. Nobody expects agencies to be unhackable. What people do expect is transparency when something like this happens, and fast action to protect the people whose information might be exposed.
Because at the end of the day – and yeah, I know, I said I wouldn’t use that phrase, but it fits here – this isn’t really about the FBI’s reputation. It’s about the actual humans who work there, whose safety just got a lot more complicated over something they had zero control over.